
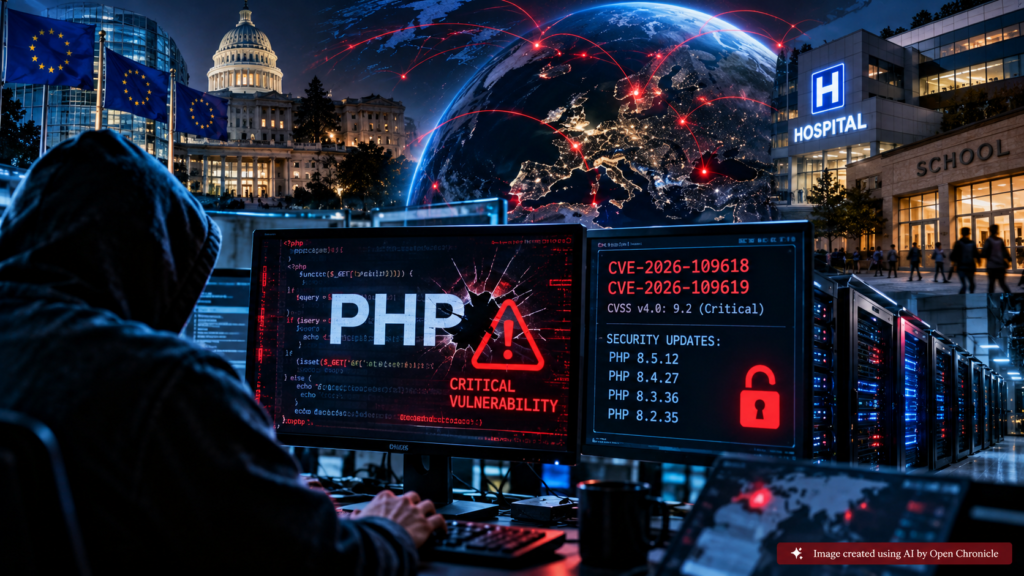
Government agencies, hospitals, schools and major online services are taking emergency precautions after critical vulnerabilities were identified in PHP, one of the world’s most widely used web programming languages. Cybersecurity authorities in Europe and the United States have issued warnings, while Cloudflare reports detecting attempts to exploit the flaws.
By Open Chronicle News Desk with Agencies
BRUSSELS / WASHINGTON — October 23, 2026
A major cybersecurity alert is spreading across Europe and the United States after artificial intelligence systems reportedly identified critical vulnerabilities in PHP, the programming language used to power a substantial portion of the world’s websites and online applications.
Government institutions, hospitals, schools and other organisations have temporarily taken websites offline while technical teams work to install security updates and assess potential exposure.
The emergency response follows reports that attackers have already begun attempting to exploit the newly disclosed vulnerabilities.
Cloudflare, one of the world’s largest internet infrastructure and cybersecurity companies, has reportedly detected early malicious activity targeting the affected software.
The incident has prompted warnings from the European Union’s Computer Emergency Response Team (CERT-EU), alongside cybersecurity guidance attributed to US security agencies, including the National Security Agency (NSA) and the Federal Bureau of Investigation (FBI).
According to reporting attributed to Reuters, CERT-EU advised organisations unable to apply the necessary security fixes promptly to consider temporarily disconnecting vulnerable websites.
The developers responsible for PHP have released updates addressing two previously identified critical vulnerabilities and urged users and system administrators to install them immediately.
The incident has also raised questions about the growing role of artificial intelligence in cybersecurity, particularly its ability to discover weaknesses in software used by millions of organisations.
Critical Vulnerabilities Discovered in PHP
At the centre of the alert are two critical security vulnerabilities affecting PHP, a widely deployed server-side programming language.
PHP is used to develop websites, online services and applications that process information on web servers.
It is particularly important because it supports major content management systems, including WordPress, as well as countless business applications and institutional websites.
Security weaknesses in PHP can therefore have consequences extending far beyond a single company or online service.
Depending on the precise nature of a vulnerability, attackers may be able to interfere with web applications, access sensitive information or compromise systems that have not been properly secured.
The supplied reports do not identify the specific vulnerability numbers, affected PHP versions or technical exploitation methods.
Those details are essential for determining which systems are vulnerable and what defensive measures are required.
Nevertheless, the widespread use of PHP explains why the discovery has triggered an international response.
Artificial Intelligence Identified the Security Weaknesses
One of the most significant aspects of the incident is the reported involvement of artificial intelligence in discovering the vulnerabilities.
According to the information provided, AI models identified security flaws that could have serious consequences for internet infrastructure.
OpenAI, the company behind ChatGPT, reportedly described the discovery as involving one of the most consequential vulnerabilities identified in recent times.
That assessment has not been independently verified against a direct company statement for this report.
Artificial intelligence is increasingly being used by cybersecurity researchers to examine software code, identify unusual behaviour and detect potential weaknesses.
Such systems can analyse large amounts of code and help researchers locate vulnerabilities that might otherwise require extensive manual investigation.
However, the same technological advances also raise concerns about malicious actors using AI to accelerate vulnerability discovery and develop attacks.
The latest incident illustrates both sides of this development.
AI-assisted research may help identify dangerous weaknesses before they cause widespread damage, but once those weaknesses become known, organisations face pressure to apply security fixes before attackers exploit them.
Cloudflare Reports Early Exploitation Attempts
Cloudflare has reportedly detected attempts to exploit the newly disclosed PHP vulnerabilities.
The company operates services that protect websites, manage internet traffic and help organisations defend against malicious requests.
Its infrastructure provides visibility into certain categories of cyberattacks affecting online services.
According to the supplied account, Cloudflare began recording malicious activity after the vulnerabilities became known.
The reports do not establish how many attacks succeeded, how many organisations were compromised or whether sensitive information was stolen.
That distinction is important.
An attempted exploit does not necessarily mean that an attacker gained access to a system.
However, the appearance of malicious traffic shortly after a vulnerability becomes public can indicate that attackers are moving quickly to target systems that remain unpatched.
For organisations operating essential services, even unsuccessful attacks can increase operational pressure and require additional security monitoring.
CERT-EU Advises Organisations to Take Vulnerable Websites Offline
The European Union’s cybersecurity response team has reportedly recommended strong precautionary measures.
According to reporting attributed to Reuters, CERT-EU advised organisations that could not implement security fixes in time to consider temporarily taking affected websites offline.
Such a recommendation reflects the potential consequences of leaving vulnerable systems accessible while attackers are actively attempting exploitation.
Taking a website offline can interrupt public services and business operations.
However, it may also reduce immediate exposure while administrators install updates, review configurations and verify that systems are secure.
The measure is particularly relevant for institutions handling sensitive information, including government agencies, healthcare providers and educational organisations.
The decision to disconnect a service depends on its exposure, operational importance and available protective measures.
A temporary shutdown does not, by itself, establish that the website has been compromised.
European Governments and Institutions Disrupt Online Services
Several European countries have reportedly taken precautionary action in response to the security alert.
The supplied reporting identifies the Netherlands, Finland, Germany, Belgium and France among the countries where government websites experienced interruptions associated with the response.
Authorities and technical teams are understood to be assessing systems and applying security updates.
In the United Kingdom, websites associated with the Scottish Government and the BBC were also reportedly affected.
The disruptions illustrate the challenge of responding to a security problem involving widely used software.
Government websites provide access to essential information, administrative services and public communications.
Temporary interruptions can therefore affect citizens, businesses and institutions that rely on those platforms.
For hospitals and schools, the operational consequences may be especially sensitive when online systems support appointments, communications, administrative records or educational services.
The supplied information does not identify all affected institutions or establish whether their disruptions resulted from confirmed attacks, precautionary shutdowns or maintenance.
NSA and FBI Issue Cybersecurity Warnings
The security incident has also prompted concern among US authorities.
According to the supplied account, the NSA and the FBI have issued recommendations highlighting the risk of data exposure and unauthorised access to internal networks.
The warnings reflect the broader danger that vulnerabilities in publicly accessible web applications can create for connected organisational systems.
A website may serve as an entry point into a larger technological environment if security controls are inadequate.
Depending on the vulnerability and the configuration of the affected server, a successful compromise could potentially expose confidential information or enable further malicious activity.
However, the available material does not establish that these consequences have occurred in any specific organisation.
The agencies’ reported guidance underscores the importance of applying official software updates, monitoring systems for suspicious activity and limiting unnecessary exposure.
Organisations are also encouraged to maintain effective incident-response procedures so they can investigate and contain any confirmed intrusion.
PHP Developers Release Emergency Security Updates
The PHP development community has reportedly made security updates available to address the two critical vulnerabilities.
Developers have urged users to apply the fixes without delay.
Security patches are one of the most important defences against publicly known software weaknesses.
Once a vulnerability is disclosed, attackers may begin scanning the internet for systems that have not yet been updated.
This creates a period of elevated risk for organisations that depend on older or unsupported software.
However, updating PHP may require compatibility testing, particularly where websites depend on plugins, custom applications or older frameworks.
Administrators must therefore balance the urgency of installing security fixes with the need to maintain reliable services.
For critical systems, a coordinated response may involve creating backups, testing updated software, applying patches and monitoring for abnormal activity.
The specific updates required depend on the affected PHP versions and the official technical advisories.
Why a PHP Vulnerability Can Affect So Much of the Internet
PHP occupies a central position in the modern web.
Unlike software installed only on individual computers, server-side programming languages operate behind websites and online applications.
Users may interact with PHP-powered services without ever knowing which technology supports them.
A vulnerability affecting a widely deployed PHP component can therefore create exposure across different industries and countries.
The potential impact is especially significant for organisations using similar software configurations or relying on shared hosting environments.
A single underlying weakness may affect numerous independent websites.
However, the presence of PHP on a server does not automatically mean that the server is vulnerable to every PHP security flaw.
Actual exposure depends on factors such as the software version, operating system, configuration and whether the affected functionality is enabled.
This distinction is essential when assessing the scale of the current incident.
Hospitals, Schools and Government Services Face Particular Risks
The reported disruption of public-sector and institutional websites has highlighted the importance of cybersecurity in essential services.
Government portals often handle identity information, administrative requests and confidential records.
Hospitals may depend on digital systems for scheduling, communications and access to patient-related services.
Schools and universities increasingly use web applications for educational resources, student administration and internal operations.
A serious vulnerability affecting these environments can create risks involving service availability, information security and public trust.
Even when organisations disconnect websites as a precaution, the interruption can affect people who rely on online services.
The current reports do not establish that hospital clinical systems, patient records or school databases have been compromised.
Nevertheless, the situation demonstrates why cybersecurity preparedness is now an essential component of public-service continuity.
The Growing Role of AI in Cybersecurity
The reported discovery of the PHP flaws by artificial intelligence marks another development in the changing relationship between AI and digital security.
Traditionally, identifying complex software vulnerabilities has required extensive manual code analysis, specialised technical knowledge and structured security testing.
AI-assisted tools can help researchers examine large codebases, detect suspicious patterns and prioritise areas requiring human investigation.
This may accelerate the discovery of vulnerabilities and allow developers to correct weaknesses before they are widely exploited.
At the same time, attackers may attempt to use similar technologies to identify vulnerable systems or automate aspects of malicious activity.
The result is a rapidly evolving cybersecurity environment in which defenders and attackers can both benefit from more powerful analytical tools.
The long-term impact will depend on how effectively organisations integrate AI-assisted security research with responsible disclosure, software maintenance and operational safeguards.
The latest reported incident provides a reminder that identifying a vulnerability is only the beginning of the defensive process.
The critical next steps are verifying the weakness, releasing reliable fixes and ensuring that affected systems receive them.
What Organisations Should Do
The immediate priority for website administrators is to determine whether their systems are affected by the vulnerabilities described in the official PHP security advisories.
Organisations should consult the PHP project’s security announcements and guidance from relevant national cybersecurity authorities.
Where applicable, security teams should install supported updates as quickly as operationally feasible.
They should also review server configurations, monitor logs for suspicious requests and investigate any indicators of compromise.
Critical services may require temporary restrictions or additional protective measures while updates are being deployed.
Maintaining reliable backups and tested recovery procedures is particularly important for institutions that cannot tolerate prolonged interruptions.
For websites using WordPress or other PHP-based applications, administrators should verify compatibility with supported PHP versions and keep their wider software environment updated.
No single precaution guarantees complete protection, but timely patching and layered security controls can significantly reduce exposure.
The Big Picture: A Global Internet Security Challenge
The reported discovery of critical PHP vulnerabilities has triggered an international response involving technology companies, software developers and government cybersecurity authorities.
European institutions have reportedly interrupted online services, while US agencies have warned about potential threats to data and internal networks.
Cloudflare’s reported detection of exploitation attempts adds urgency to the response.
The involvement of artificial intelligence in identifying the weaknesses also raises broader questions about the future of software security.
As AI becomes more capable of examining complex systems, vulnerabilities may be discovered faster than organisations can deploy updates.
That imbalance could create significant challenges for governments, businesses and critical infrastructure operators.
Three issues will determine the wider consequences of the current alert: the number of systems actually exposed, the speed at which security patches are installed and whether attackers succeed in compromising vulnerable services.
For now, the reported emergency measures illustrate the dependence of modern society on software components that often remain invisible to ordinary internet users.
The incident is a warning that a security weakness in widely deployed technology can rapidly become an international concern, making coordinated vulnerability disclosure, rapid patching and resilient digital infrastructure increasingly important.
Verified Technical Update
The official PHP security advisory confirms that two critical vulnerabilities,
CVE-2026-109618 and
CVE-2026-109619,
can permit unauthenticated remote code execution. Both were rated
9.2 under CVSS v4.0.
CVE-2026-109618 / CVE-2026-109619
Critical — CVSS v4.0: 9.2
Unauthenticated remote code execution
October 21, 2026
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35
Security updates released on October 21 include
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
The PHP development team states that updating is the only complete mitigation.
Reuters also reported that Cloudflare observed millions of exploitation attempts following public disclosure.
This does not mean millions of successful compromises.
Sources and Further Reading
PHP Development Team — Official Security Advisory
Official PHP security announcements and release information, providing technical references for software vulnerabilities, security fixes and recommended updates.
Reuters — Websites Taken Offline Over PHP Risks
Reuters reporting on precautionary website shutdowns and service disruptions associated with the PHP security alert, including responses by public institutions and other organisations.
Reuters — Cloudflare Sees Millions of Exploit Attempts
Reuters reporting on Cloudflare’s detection of exploitation attempts following the disclosure of PHP vulnerabilities, highlighting the speed and scale of malicious activity targeting potentially exposed systems.
Reuters — AI-Discovered Bugs May Trigger Further Disruptions
Reuters analysis examining how artificial intelligence-assisted vulnerability discovery could accelerate the identification of software weaknesses and create new challenges for cybersecurity teams, technology providers and critical digital infrastructure.
Editorial Note
This article is an original Open Chronicle news synthesis based on supplied reporting and official PHP security announcements dated October 20–23, 2026. Confirmed software vulnerabilities and released security updates are distinguished from reports of website disruptions, exploitation attempts and statements attributed to cybersecurity authorities. The number of attempted attacks should not be interpreted as the number of successful intrusions. The security status of individual organisations may change as updates are deployed and investigations continue.