
CYBERSECURITY | CRITICAL SECURITY UPDATE | 23 OCTOBER 2026
Two critical flaws in PHP’s core runtime have triggered emergency security updates across the web. As exploitation attempts multiply, the incident highlights the risks of memory corruption, shared server infrastructure and delayed patching.
By Open Chronicle Cybersecurity Desk
A security crisis at the heart of the web
A pair of critical security vulnerabilities in PHP, one of the programming languages underpinning a substantial part of the modern web, has prompted urgent patching efforts by website operators, hosting companies, government institutions and enterprise security teams.
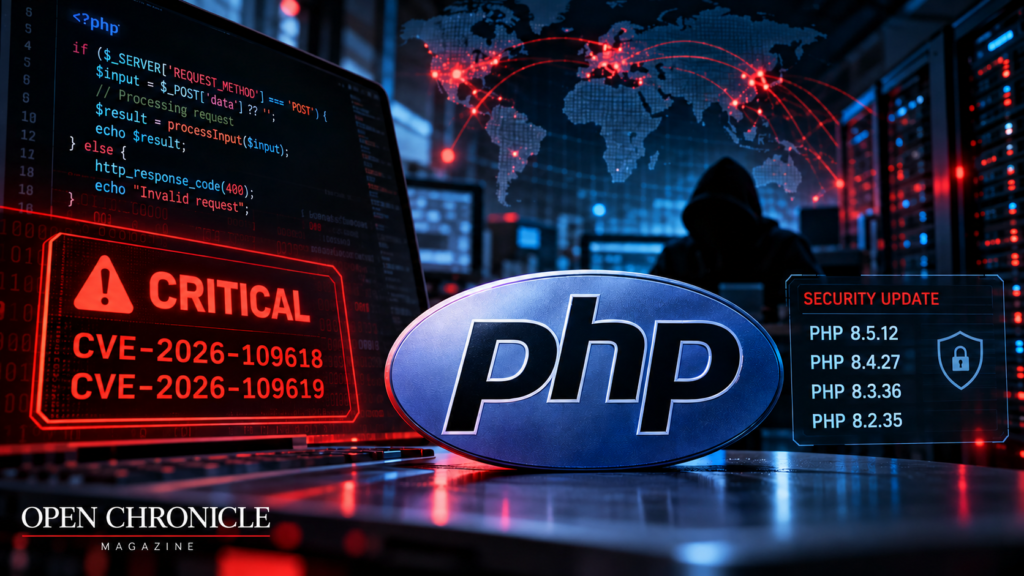
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, affect PHP’s internal handling of memory and request processing. Both received a severity rating of 9.2 under the Common Vulnerability Scoring System version 4.0 (CVSS v4.0).
Their most serious potential consequence is unauthenticated remote code execution: under vulnerable conditions, an attacker may be able to cause a server to execute code without first obtaining legitimate login credentials.
On 21 October 2026, the PHP development team released emergency security updates for four supported branches: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
The project warned that configuration changes and defensive filtering could not provide a complete remedy. Updating the affected runtime was the only complete mitigation identified by the maintainers.
The urgency increased when Cloudflare reported a rapid escalation in exploitation attempts following public disclosure. Reuters reported that activity observed across Cloudflare’s network grew from thousands of attempts before the announcement to millions afterward.
The distinction between attempted exploitation and confirmed compromise is essential. The reported figures describe hostile requests or attempted attacks, not verified successful intrusions into millions of servers.
Nevertheless, the scale of the activity demonstrates how quickly attackers can respond when a widely deployed software component becomes the subject of a critical security disclosure.
Verified technical security summary
Critical
These versions are reported in the PHP project’s security announcements. Vendor-maintained packages may use different version numbering or backported fixes.
1. Why PHP matters to Internet security
PHP is a server-side programming language used to generate dynamic web content, process requests, interact with databases and support complex web applications.
When a visitor opens a PHP-powered website, the web server may invoke the PHP runtime to process application instructions and return the resulting page.
This architecture supports everything from simple publishing systems to major commercial services.
PHP is particularly important to content management systems, including WordPress, Drupal and Joomla, as well as numerous e-commerce platforms and custom business applications.
The distinction between an application vulnerability and a language-runtime vulnerability is significant.
A flaw in a particular WordPress plugin might expose only installations using that plugin. A vulnerability in PHP itself can affect different applications that depend on the same vulnerable runtime, even if their own code is correctly written.
This does not mean every PHP website is automatically exploitable. Exposure depends on the installed version, the server configuration, the execution environment and whether the conditions required for exploitation can be reached.
However, the potential attack surface is unusually broad.
The PHP security advisory explicitly identifies web-serving installations using PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed as environments requiring attention.
For organisations operating multiple websites or shared hosting platforms, a single vulnerable PHP component can create a security concern across numerous services.
2. CVE-2026-109618 — Memory corruption during out-of-memory handling
The first vulnerability, CVE-2026-109618, involves the way PHP responds when a request encounters an out-of-memory condition.
Software normally allocates memory as it processes information. When an operation fails because a memory limit has been reached, the program must terminate or recover while ensuring that internal resources remain in a valid state.
That recovery process is particularly sensitive in low-level software written in memory-unsafe languages.
According to the technical advisory, PHP’s error-handling mechanism can interrupt execution while internal request structures are only partially initialised.
Subsequent cleanup operations may then interpret incomplete or invalid memory structures as though they were valid.
In simplified terms, the runtime may attempt to release or manipulate memory using information that was never safely established.
Under carefully controlled conditions, such memory corruption can create opportunities for an attacker to influence program execution.
This is why the vulnerability is more serious than an ordinary application error or temporary server crash.
The danger arises not merely because a request fails, but because the failure can leave internal memory management in an unsafe condition.
An attacker who can trigger the vulnerable sequence may be able to exploit that state to achieve consequences beyond the intended behaviour of the PHP application.
3. CVE-2026-109619 — Dangerous state surviving between requests
The second vulnerability, CVE-2026-109619, concerns stale global state.
A web server may process many requests through long-running worker processes. Each request should begin with the internal state needed for safe execution.
Some information is specific to one request and should not remain usable after that request has ended.
The vulnerability arises when internal state associated with a request survives after the memory supporting it has been released.
If a later request accesses that stale state before it is properly reset, the runtime may interact with memory that no longer contains the expected information.
This type of error is related to a broader family of memory-safety problems involving invalid references and use of memory after its lifetime has ended.
The consequences can include crashes, unexpected data exposure or, under exploitable conditions, execution of attacker-controlled code.
The important security principle is that the boundaries between successive web requests must remain reliable.
When request-specific state is not fully isolated or reset, an attacker may gain opportunities to influence behaviour across those boundaries.
For servers processing large volumes of public traffic, failures of this kind are especially concerning.
4. Why unauthenticated remote code execution is so dangerous
Remote code execution, commonly abbreviated RCE, describes a situation in which an attacker can cause a target system to execute instructions outside its intended security boundaries.
The term unauthenticated means that exploitation does not necessarily require the attacker to possess a legitimate user account.
This changes the risk considerably.
Many attacks against web applications begin with stolen credentials, compromised administrator accounts or flaws in application-level authentication.
An unauthenticated runtime vulnerability may expose a lower-level component before those application protections become relevant.
The PHP development team specifically identified Apache mod_php as a particularly concerning environment because a demonstrated exploit could be triggered by an unauthenticated request before application code executed.
If successful exploitation occurs, the consequences depend on the permissions of the affected process and the surrounding system.
Possible outcomes include access to sensitive application files, theft of configuration secrets, interference with website operations, installation of malicious software or attempts to move into connected systems.
A compromised web-server process does not automatically grant an attacker unrestricted control over an entire organisation. Operating-system permissions, isolation mechanisms and network segmentation can limit what an attacker can do.
Even so, code execution within a production web environment represents a serious breach of the system’s intended trust boundaries.
5. Why the vulnerabilities affect more than one type of PHP server
PHP can be deployed through several different server architectures.
In a PHP-FPM configuration, a web server typically passes requests to dedicated PHP worker processes.
With Apache mod_php, the PHP interpreter operates within Apache’s process environment.
Other deployment models include php-cgi, LiteSpeed integrations and newer application-serving approaches such as FrankenPHP.
These architectures differ in process management, request handling, isolation and operational characteristics.
However, they can share the same vulnerable PHP runtime code.
That common dependency explains why a security flaw inside PHP may affect multiple server technologies rather than a single hosting product.
The exact exploitation conditions may differ between configurations. A demonstrated exploit in one environment should not automatically be assumed to operate identically in every other environment.
For defenders, however, the appropriate response is not to assume safety merely because a server does not use Apache mod_php.
The official advisory identifies the broader PHP web-serving ecosystem as requiring immediate attention.
6. The exploitation surge — What Cloudflare actually observed
One of the most striking developments following disclosure was the speed with which hostile activity increased.
According to Reuters, Cloudflare chief executive Matthew Prince reported that the company’s network had observed thousands of exploitation attempts before the public announcement.
The volume then rose rapidly after disclosure, reaching tens of thousands within approximately 45 minutes, hundreds of thousands within two hours and eventually millions.
These observations provide a snapshot of the reaction across a major Internet infrastructure provider.
They do not establish that millions of individual websites were successfully compromised.
A single attacker may send many requests. Automated scanners can target the same system repeatedly. Some traffic may consist of probes that fail to reach vulnerable software or do not satisfy the conditions necessary for exploitation.
Nor can attempted exploitation alone establish whether a payload succeeded.
Confirmed compromise requires additional evidence, such as forensic artefacts, unexpected process execution, malicious file changes, authenticated incident findings or other reliable indicators.
Nevertheless, the rapid increase in activity is important.
It demonstrates how the time between vulnerability disclosure and widespread automated probing can be extremely short.
For organisations with exposed infrastructure, a patching process measured in days may leave a substantial window of opportunity for attackers.
7. The role of artificial intelligence in discovering the vulnerabilities
The incident also raises an important question about the changing relationship between artificial intelligence and cybersecurity.
Google Cloud disclosed that Wiz Research had used a combination of AI models in the investigation of the PHP vulnerabilities. According to Google’s account, Gemini 4 Argon contributed to vulnerability discovery, exploit development, attack detection and patch validation.
This is a significant development, but it should be interpreted carefully.
AI-assisted vulnerability research does not mean that an artificial intelligence system independently discovered, verified and resolved every aspect of the flaws without human involvement.
Modern vulnerability research involves several stages: identifying suspicious behaviour, analysing source code, determining whether an issue is exploitable, evaluating its security impact and developing a reliable correction.
AI tools can assist researchers at different points in that process.
For example, they may help identify unusual relationships between functions, suggest test cases, compare execution paths or analyse complex code structures.
However, generated findings still require technical validation. AI systems can produce incorrect interpretations, overlook contextual constraints or propose vulnerabilities that cannot actually be exploited.
The PHP incident demonstrates both the defensive promise and the potential risks of increasingly capable automated security research.
The same techniques that help defenders identify previously unknown weaknesses can also reduce the time needed to investigate newly disclosed vulnerabilities.
This creates pressure on software maintainers and organisations to shorten the interval between discovery, disclosure and deployment of security fixes.
8. Emergency patching — Which PHP versions are affected?
The PHP project’s October 21 security release addressed the vulnerabilities in four maintained version branches.
| PHP branch | Vulnerable upstream versions | Fixed release |
|---|---|---|
| PHP 8.5 | Earlier than 8.5.12 | 8.5.12 |
| PHP 8.4 | Earlier than 8.4.27 | 8.4.27 |
| PHP 8.3 | Earlier than 8.3.36 | 8.3.36 |
| PHP 8.2 | Earlier than 8.2.35 | 8.2.35 |
| PHP 8.1 and older | No regular upstream security support | Vendor backport or upgrade required |
The distinction between upstream releases and vendor-maintained packages is important.
Some Linux distributions and enterprise support providers incorporate security fixes into existing package versions rather than adopting the latest upstream version number.
Consequently, an administrator should not determine whether a system is protected solely by comparing the displayed PHP version with the numbers above.
The installed package’s security advisory, vendor changelog and patch status must also be checked.
The PHP team has additionally made limited source backports available for certain older branches, although these do not restore full upstream support.
PHP 8.2 is approaching its scheduled end of upstream security support on 31 December 2026, making migration planning particularly important for organisations that still depend on it.
9. What website administrators should do immediately
The priority is to identify affected systems, install the appropriate security fixes and determine whether suspicious activity occurred before remediation.
Operational checklist
0 / 8 completed
For organisations using managed hosting, the PHP runtime may be controlled by the provider rather than the website administrator.
In such cases, the relevant action is to obtain confirmation that the hosting environment has received the appropriate fix.
For self-managed servers, administrators must verify that the corrected runtime is actually running after the update.
A package installation alone does not necessarily mean that existing worker processes have been restarted.
Where exploitation is suspected, incident-response procedures should take precedence over routine maintenance. Preserving relevant evidence, reviewing process activity and assessing possible credential exposure may be necessary.
10. Why firewalls and configuration changes are not complete solutions
Web application firewalls, request filtering, rate limits and network restrictions can reduce exposure to certain attack techniques.
However, the PHP maintainers explicitly warned that no complete configuration-based mitigation exists for these vulnerabilities.
The official advisory describes temporary measures addressing particular exploitation paths, including changes to memory handling, request-size restrictions and selected PHP settings.
Such measures may be useful when an organisation cannot install a security update immediately.
But they are not equivalent to correcting the underlying vulnerabilities.
An attacker may find another route to the same unsafe internal condition, and some protective settings may introduce operational or availability consequences of their own.
This is why emergency mitigations should be treated as temporary risk-reduction measures rather than permanent fixes.
For particularly exposed systems that cannot be patched, restricting or temporarily suspending public access may be necessary until remediation is completed.
The central security principle remains straightforward: patching the vulnerable runtime is the definitive remediation identified by the PHP project.
11. What the incident means for WordPress and other content management systems
The incident has particular relevance for websites built with WordPress and other PHP-based content management systems.
A website can have an updated WordPress installation, updated themes and updated plugins while still relying on a vulnerable PHP runtime.
These are separate layers of software.
WordPress updates address vulnerabilities and bugs within WordPress itself. PHP security updates address weaknesses in the language runtime on which WordPress depends.
An organisation therefore needs to maintain both.
For website owners using managed hosting, the first step is to inspect the PHP version reported by the hosting control panel and obtain confirmation that the provider has applied the relevant security fix.
WordPress’s Site Health information may help identify the PHP version, but the hosting provider remains the authoritative source for vendor patches and backported fixes.
Website owners should also ensure that backups are available and that important functions — publishing, forms, payment systems, authentication and scheduled tasks — continue working after the update.
This incident does not establish that WordPress itself contains either of the two vulnerabilities.
It demonstrates that an otherwise properly maintained application can remain exposed through a lower-level software dependency.
12. A wider warning about software supply chains
The PHP vulnerabilities illustrate a broader challenge in modern cybersecurity: the security of a digital service depends on more than the code written by its immediate developers.
A typical website may rely on an operating system, web server, language runtime, application framework, database, third-party libraries and external services.
A vulnerability in any sufficiently privileged component can affect the security of the whole system.
This creates a form of inherited risk.
Organisations may have strong internal development practices but remain exposed to vulnerabilities in software maintained by external projects.
Open-source software plays an essential role in the Internet’s infrastructure, and its widespread use brings substantial benefits in accessibility, interoperability and innovation.
Yet the same widespread adoption means that critical vulnerabilities can have consequences across many organisations simultaneously.
The speed of the response becomes especially important when attackers can automate vulnerability discovery and exploitation attempts.
Maintaining accurate software inventories, monitoring upstream security advisories and preparing reliable emergency-update procedures are therefore essential parts of operational resilience.
13. The next phase — From emergency response to long-term resilience
As organisations deploy the October 21 patches, attention must shift toward verifying remediation and assessing possible exposure during the interval before systems were updated.
Security teams should distinguish between three separate questions.
First, was the organisation running an affected PHP version?
Second, was the vulnerable runtime accessible through a configuration that could permit exploitation?
Third, is there evidence that an attacker successfully exploited the vulnerability?
An affirmative answer to the first question does not automatically establish the second or third.
Likewise, the absence of an obvious website outage does not prove that a system was never compromised.
The appropriate investigation depends on the environment, available logs, security monitoring and the organisation’s risk profile.
The incident also reinforces the importance of reducing unnecessary privileges for web-server processes, isolating workloads and limiting access to sensitive systems.
These measures cannot replace security updates, but they can reduce the consequences of a successful intrusion.
Conclusion — A critical reminder of the Internet’s shared vulnerabilities
The discovery of CVE-2026-109618 and CVE-2026-109619 represents a significant security event because the flaws affect a foundational component of web infrastructure.
Their severity arises from the possibility of unauthenticated remote code execution, the breadth of PHP deployment and the complexity of the memory-management errors involved.
The rapid increase in exploitation attempts following disclosure demonstrates how quickly attackers can react to newly available technical information.
Yet the reported scale of attempted attacks should not be confused with confirmed widespread compromise.
The immediate priority for organisations is clear: identify vulnerable installations, apply verified security fixes and investigate suspicious activity where appropriate.
The broader lesson extends beyond PHP.
Modern digital security depends on the integrity of software components that users rarely see, administrators may not directly control and organisations sometimes overlook.
A website is only as secure as the systems that execute its code.
Sources and Further Reading
The following sources support the technical findings, security recommendations and reported developments in this article.
PHP Development Team — Critical Remote Code Execution Security Advisory
Official details of the two vulnerabilities, affected execution environments, patched versions and emergency mitigation guidance.
CERT-EU — Critical Vulnerabilities in PHP
European institutional security advisory covering the technical mechanisms, severity, affected installations and recommended response.
Google Cloud — Responding to Core PHP Vulnerabilities
Technical commentary on the discovery process, AI-assisted security research and defensive response.
Reuters — Cloudflare Sees Millions of Exploit Attempts After PHP Disclosure
Reporting on the escalation of attempted exploitation, Cloudflare’s observations and the wider operational response. The reported attempts do not establish an equivalent number of successful compromises.
cPanel — Critical PHP Security Release
Vendor-specific information about affected hosting environments, patched package versions and update procedures.
This article is based on publicly available security advisories, technical documentation and reporting available as of 23 October 2026. Vulnerability exploitation conditions, vendor remediation status and incident assessments may change as investigations continue. References to exploitation attempts do not imply confirmed successful compromises.
Understanding the systems behind the headlines.
Explore Open Chronicle Explained →